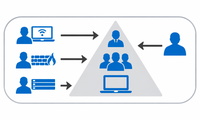
Two products, one way to secure every application with Active Directory
Whichever directory your organization runs, on-premises or in the cloud, each application gets the same thing: a simple JSON API to authenticate users and check their roles, instead of its own password list.
Active.Directory.Utility
On-premises Active Directory
For organizations running their own domain controllers. Runs on Windows IIS and talks to Active Directory over PowerShell, WinRM/SSL and LDAPS, built on the latest version of .NET and the latest Active Directory PowerShell module.
Active.Directory.Utility.Entra
Cloud-based Microsoft Entra ID
For organizations using Microsoft Entra ID (Azure AD) in the cloud. Authenticates with a certificate, a managed identity, or a client secret, built on the latest version of .NET and the latest Microsoft Entra and Microsoft Graph PowerShell modules.
Built around one main use case: role-based security
Both products exist to do the same job: let any application, written in any language, decide what a signed-in person may do by checking the groups they belong to in your directory — on-premises Active Directory for one product, Microsoft Entra ID for the other. Add someone to a group, or remove them, and every application that checks it sees the change immediately. No per-application user lists, no roles to keep in sync by hand.
Simple
Plain JSON in, plain JSON out. Every method is documented in Swagger.
Secure
HTTPS only, API key required, encrypted secrets and full audit logging.
Any application
Web, desktop and mobile back ends, internal tools, ERP and HR systems, ticketing, scripts and services.